Verify the package archive
Tapid compares supported downloads with the checksum published by the registry. A mismatch stops the install.
A package install brings someone else's code into your project. Tapid verifies the download, records the exact dependency tree, and keeps install scripts from running on their own.
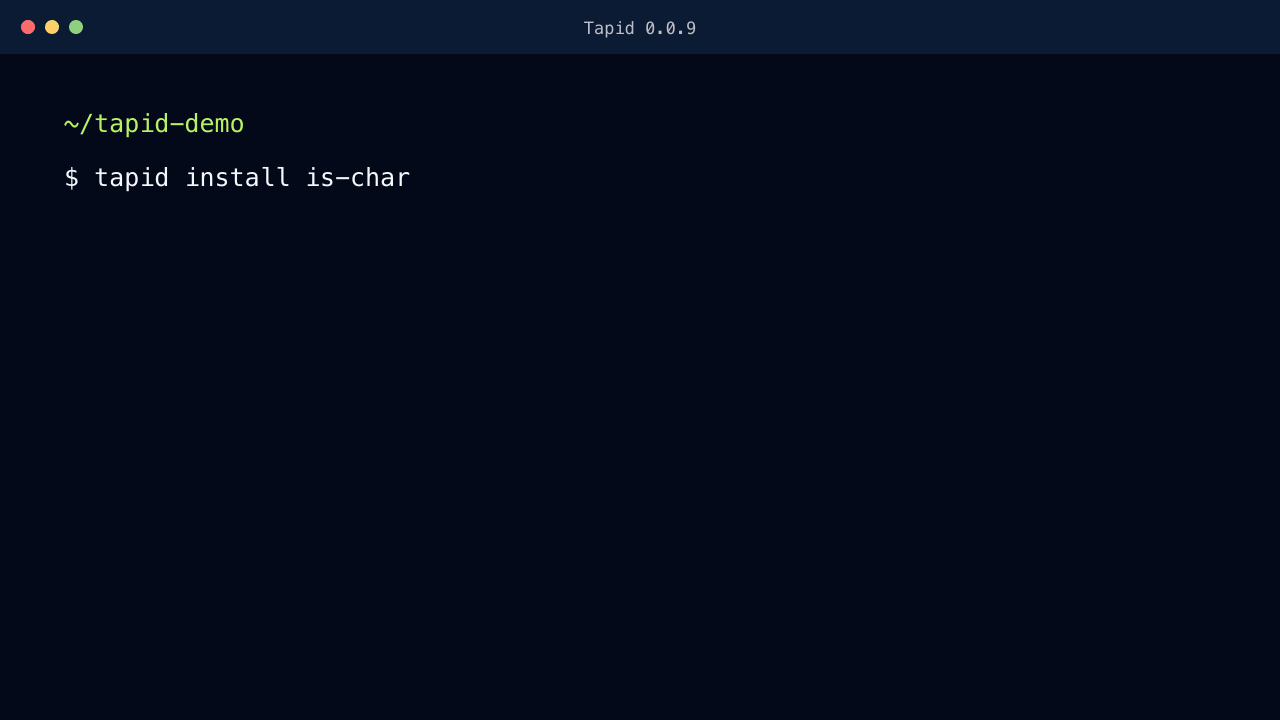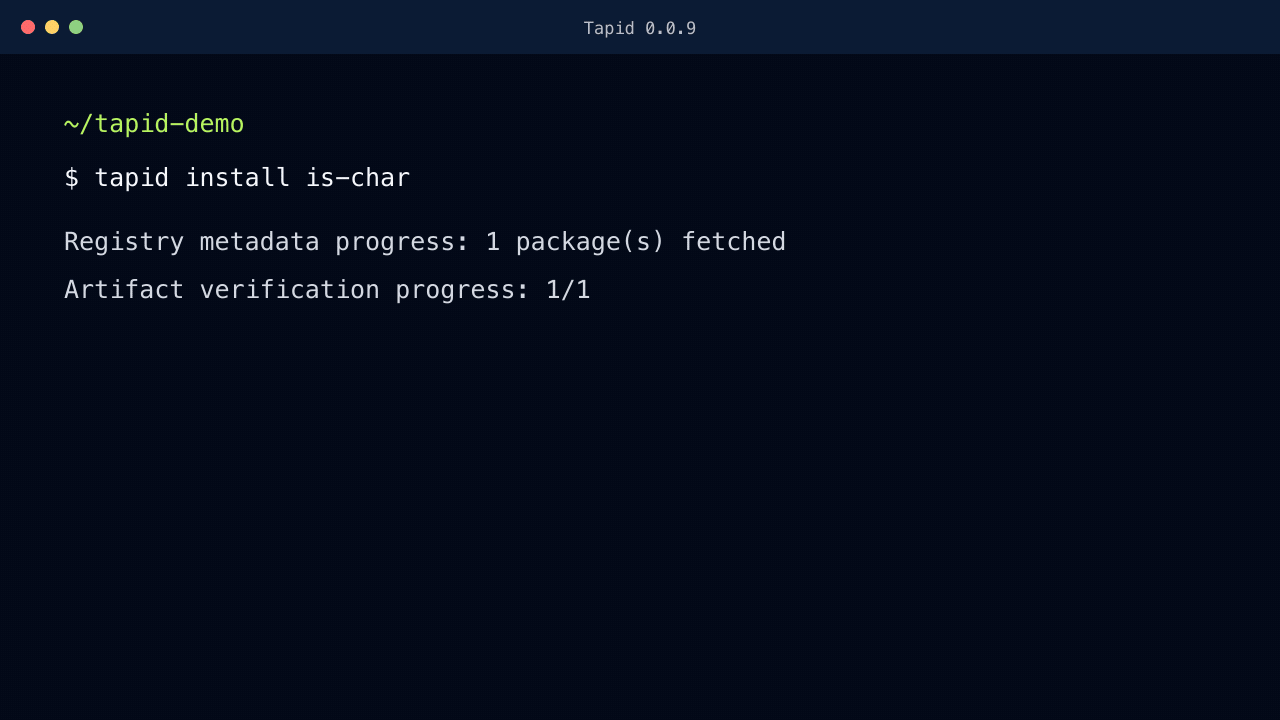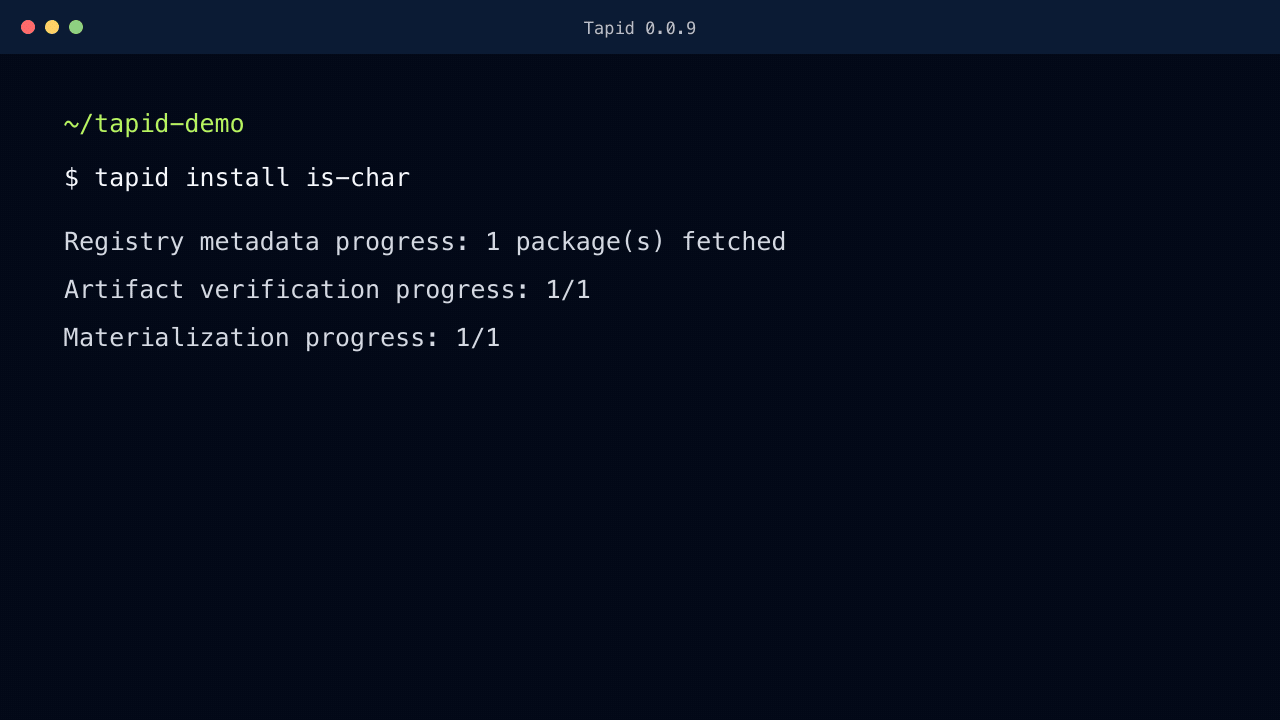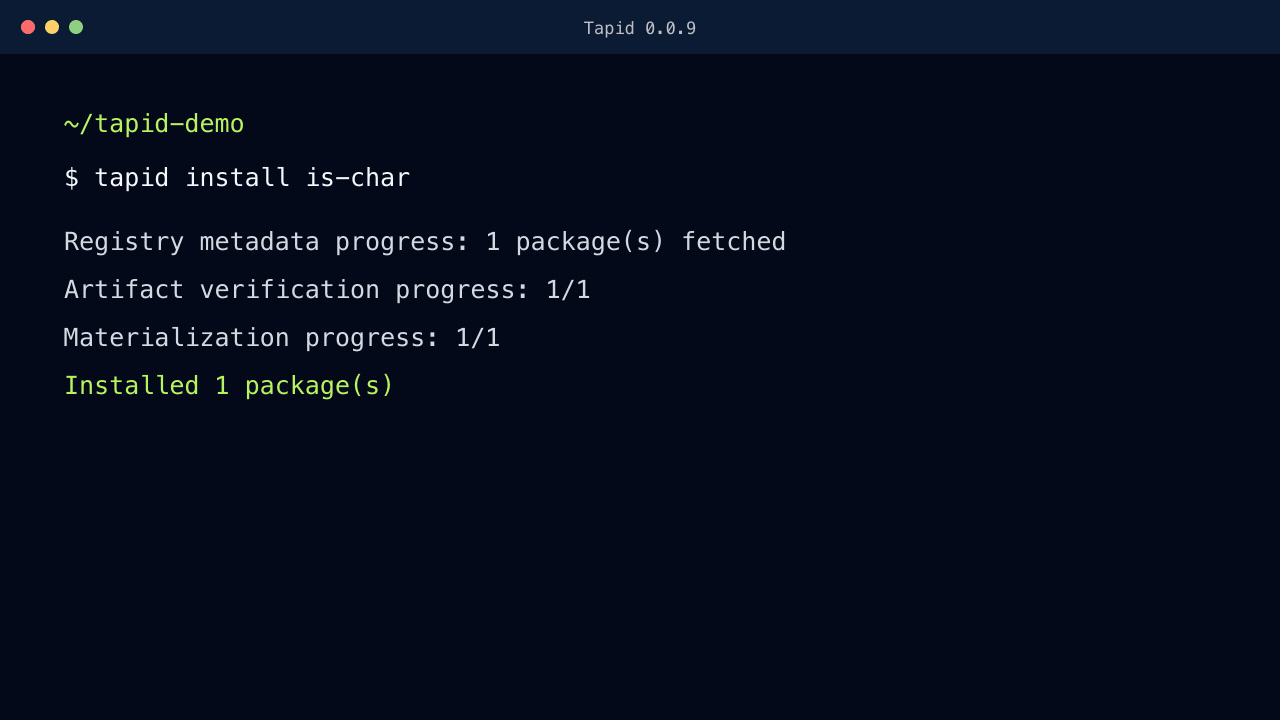
Tapid is a package manager that makes dependency installation controlled and inspectable.
Tapid compares supported downloads with the checksum published by the registry. A mismatch stops the install.
tapid.lock records exact package versions and relationships so the project has an inspectable installation record.
Dependency lifecycle scripts do not run automatically while Tapid installs a package.
Coding agents can request a named package and version through the same controlled installation path a developer uses.
An agent can add a dependency in seconds. Tapid makes the install inspectable. It verifies the download, keeps dependency scripts disabled, writes the dependency tree to tapid.lock, and can check that record before the project is reused.
AI malware scanning is in development. The current CLI does not claim that a matching package is safe.
Read about Tapid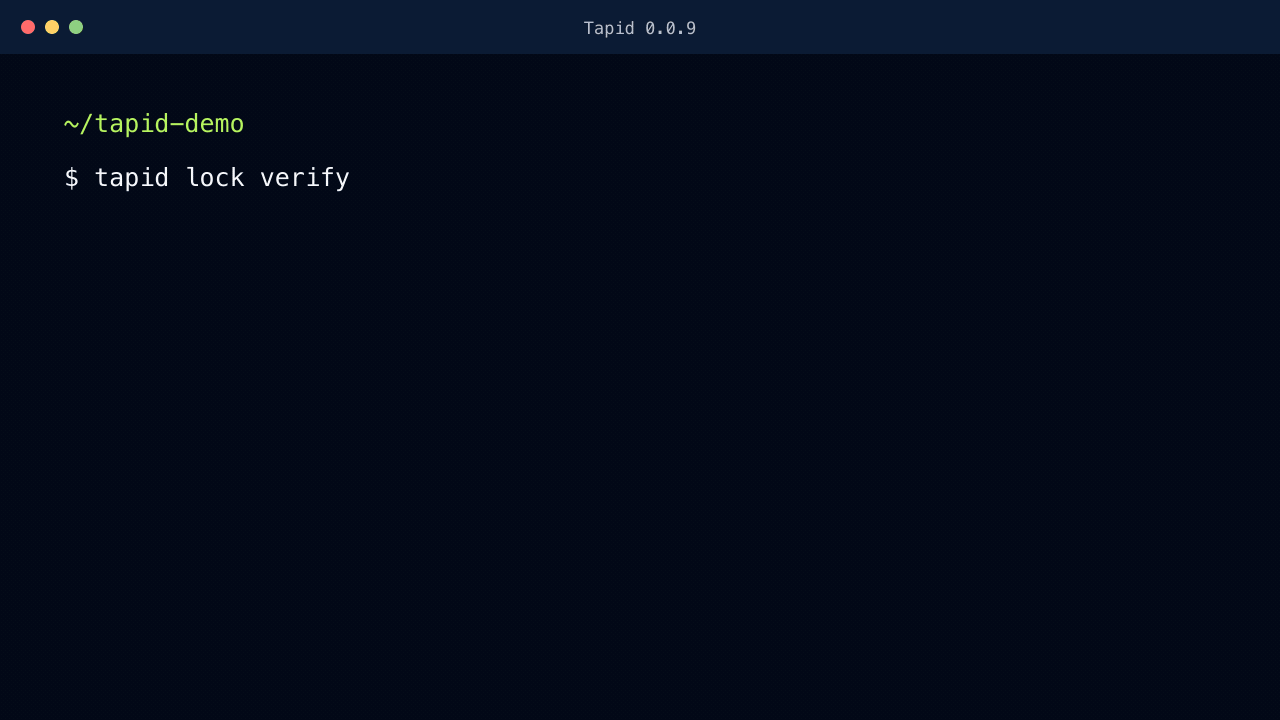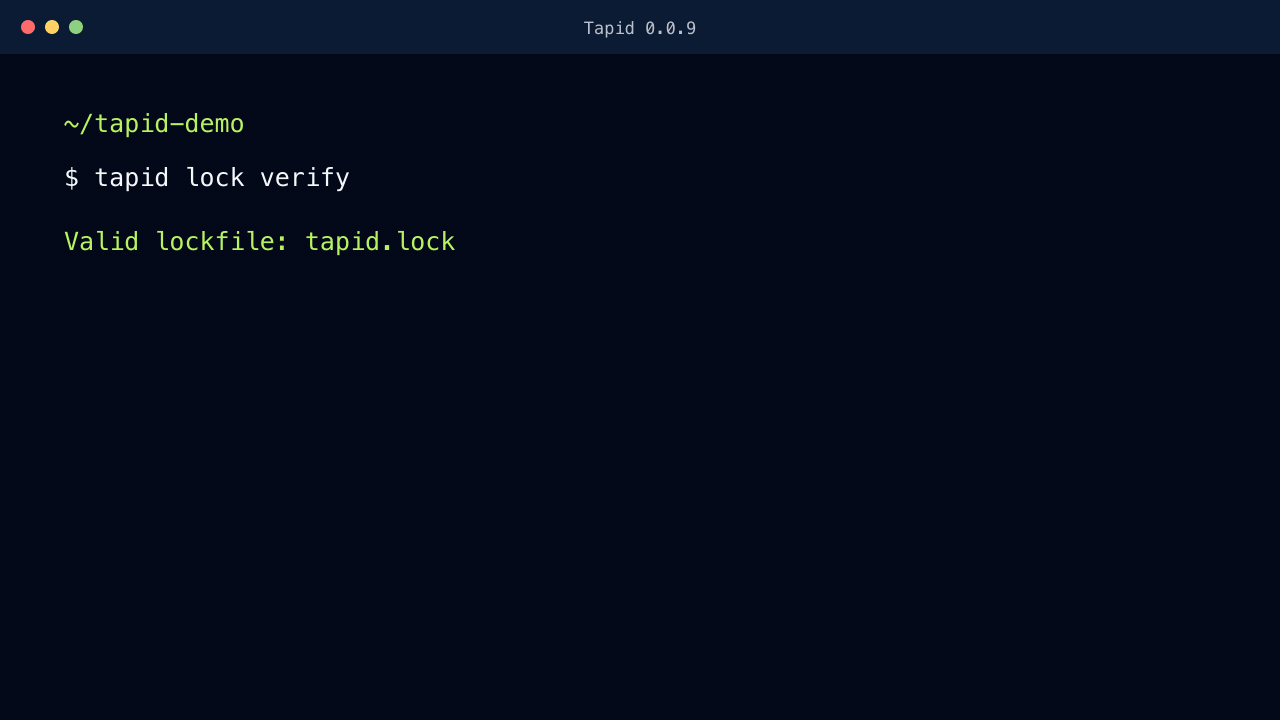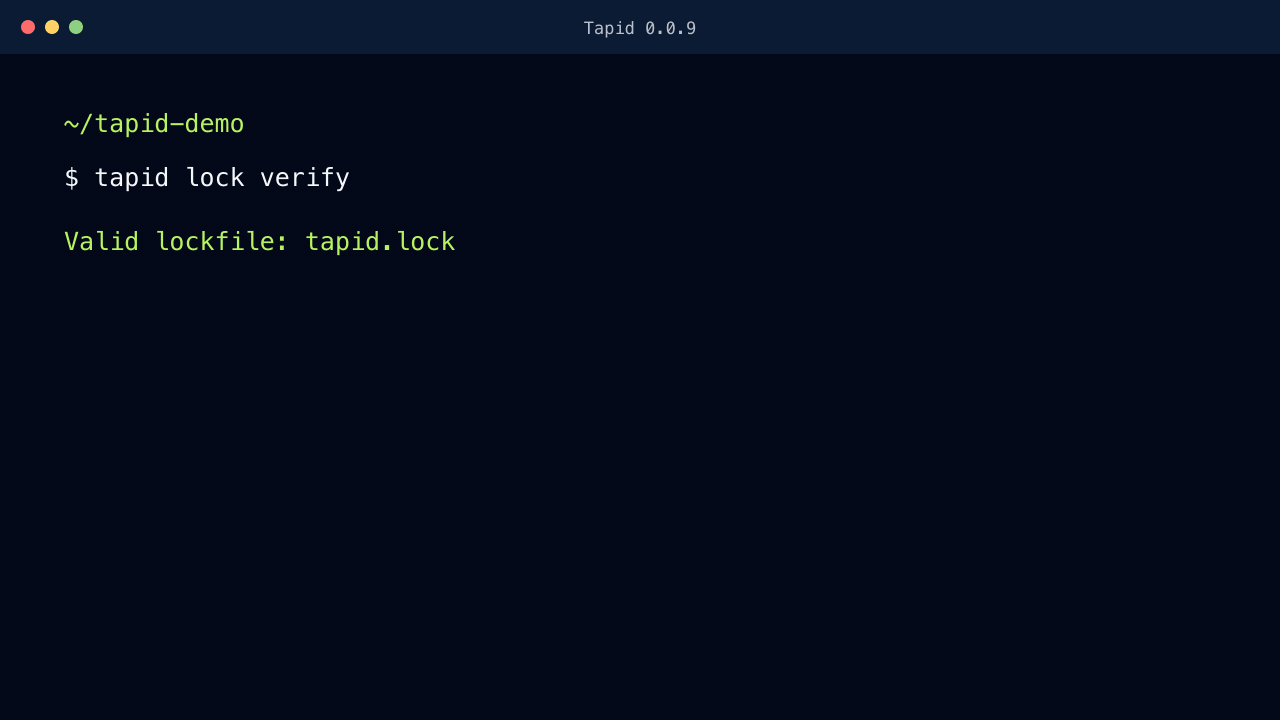
The useful workflow depends on what you are responsible for and how many people need to trust the result.
A solo developer cannot review every line in every package release. Tapid checks the download against the registry checksum, records the exact dependencies used, and leaves dependency install scripts disabled. That does not prove the code is safe, but it makes every install easier to inspect and reproduce.
See how Tapid installs packagesAs a team grows, coding agents may update dependencies before anyone has reviewed what enters the project. Tapid gives agents a controlled installation path and shows developers what changed since the previous version, so the change can be reviewed before it becomes part of the build.
See the Tapid workflowA lockfile records the exact packages and dependency relationships Tapid installed. Teams can inspect that record, keep it with the project, and verify it before reusing the same inputs in another environment.
Read about reproducible installsStart with the free Tapid CLI. Verify downloads, record exact dependencies, and review changes before they reach your project.
Get the free CLI